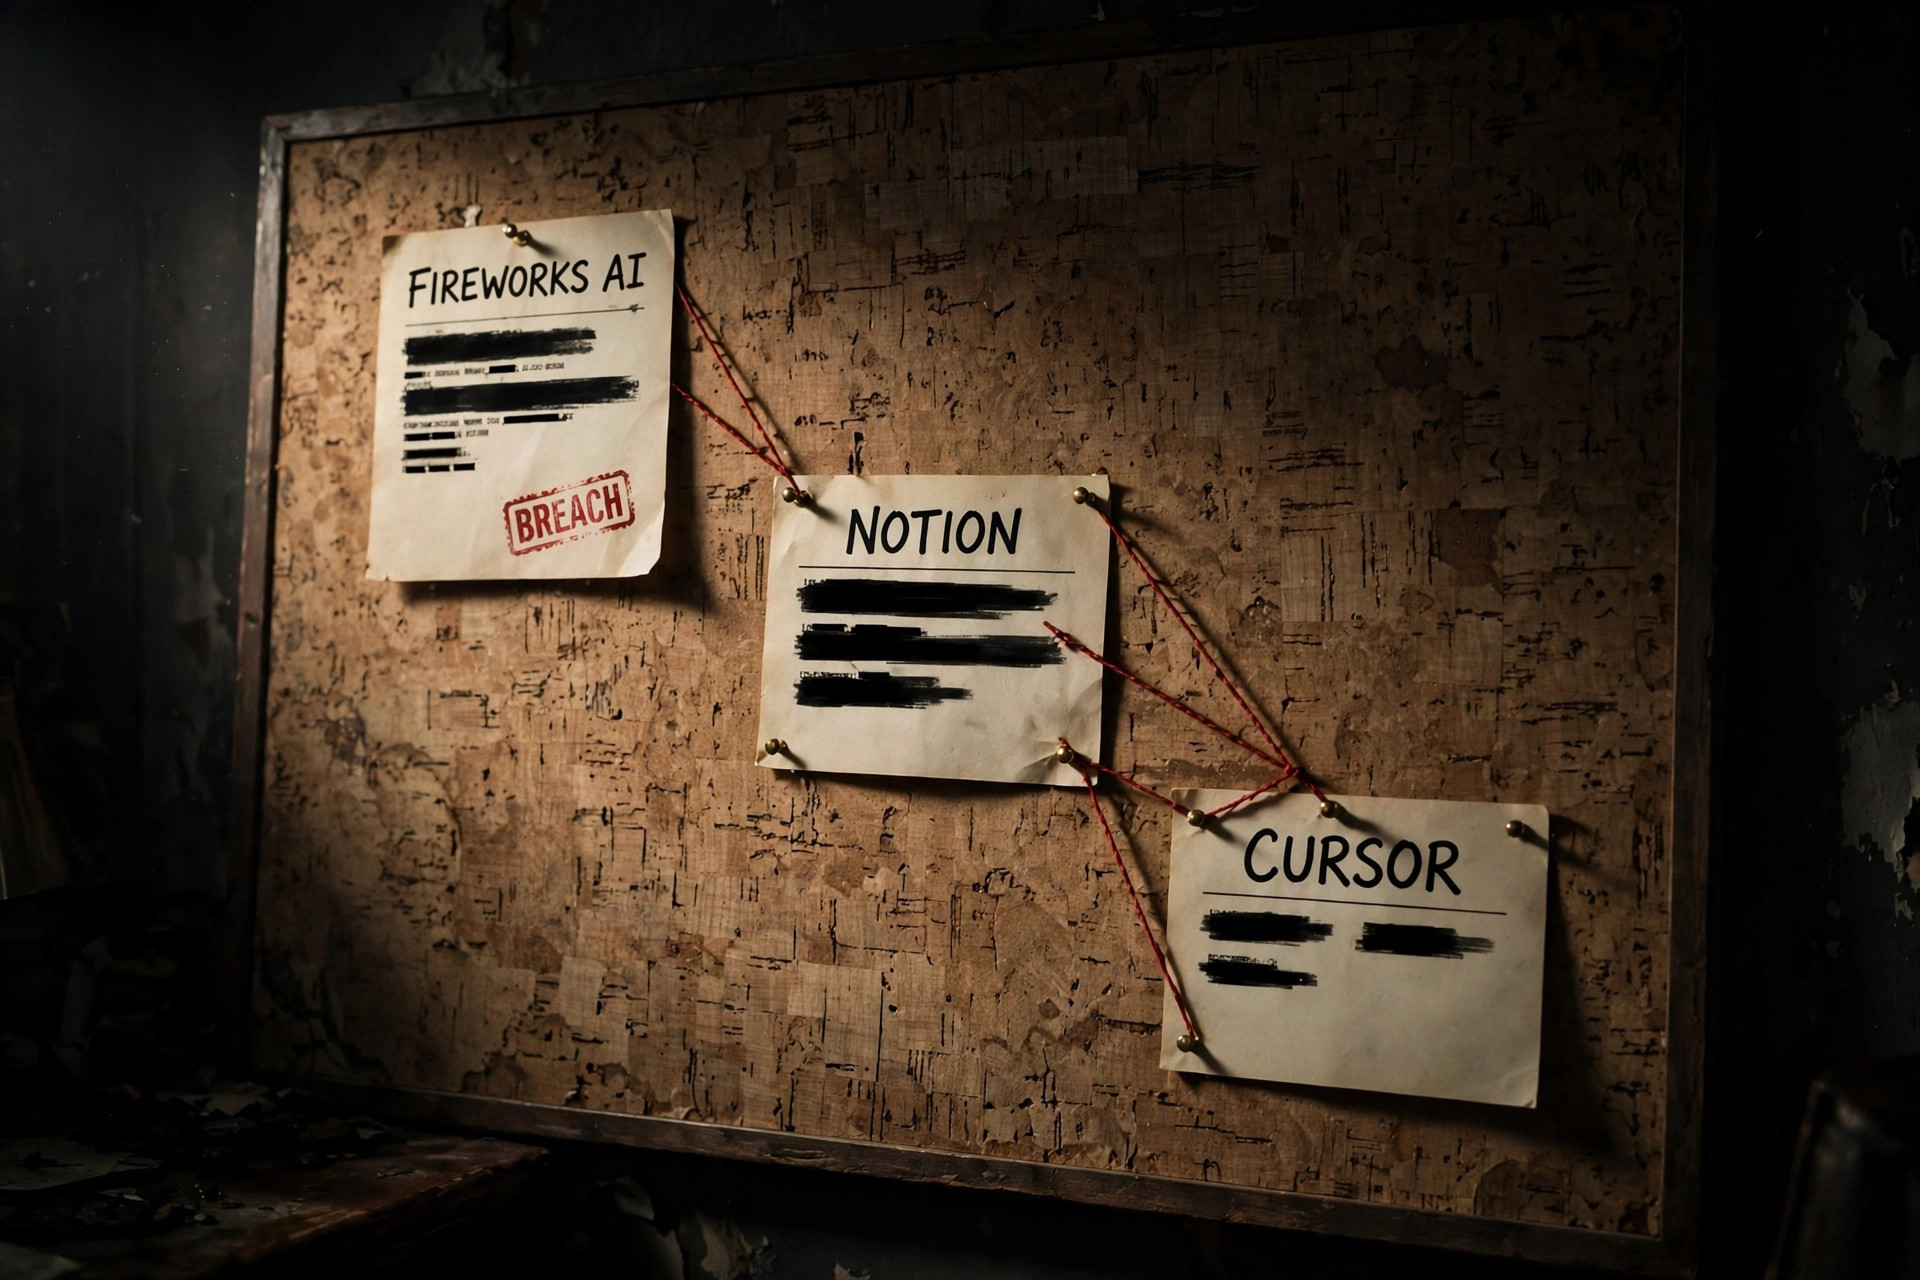
One vendor’s bad month became three companies’ incident. Fireworks AI, the inference platform, was breached twice in October 2026. The fallout reached Notion and Cursor, two of its customers, and the last hop put malware in front of developers.
The 97-second reel: one key, three companies, told as an evidence board.
Two breaches in seventeen days
On October 6, Fireworks spotted unauthorized use of its internal credentials. That was breach one. On October 23, a second breach began at its cloud provider, and a day later an unauthorized workload ran on Fireworks development machines. Billing data was exposed, along with incomplete model weights and datasets for some customers.
The Notion hop
Notion says under 1% of workspaces had unattributable AI chat transcripts exposed through its Insights feature. The chats reached Fireworks as part of normal product plumbing. When Fireworks was breached, data Notion users never sent to Fireworks directly was sitting inside the blast radius.
The Cursor hop
Cursor had given Fireworks a key. That key leaked, and it opened a read-only storage bucket holding limited non-Privacy-Mode coding-agent traces. The attacker copied traces that included unredacted API credentials for under 0.01% of Cursor customers. Read-only access to the bucket did not mean read-only consequences.
Eleven hours of malware
On October 29, the attacker used a stolen credential taken from the exposed data of Cursor’s internal system to place a trojanized Claude Code extension, versions 2.1.312 and 2.1.313, into Cursor’s marketplace cache. It sat there for about eleven hours and could have reached up to 5,000 users. A breach at an inference vendor ended as a supply chain attack on a code editor’s marketplace.
The audit
Three steps, in order. Remove Claude Code extension 2.1.312 and 2.1.313 if they are installed, and rotate your keys. Turn on trace Privacy Mode in your coding agent so session traces stop leaving your machine with credentials inside. Inventory every vendor key you have issued and every key a vendor holds for you, because the chain above ran on keys moving between companies, not on anyone’s front door getting kicked in.
Caveats
The exposure percentages are the companies’ own figures as reported by The Hacker News and BleepingComputer in November 2026. “Potentially reaching up to 5,000 users” is the reported ceiling for the trojanized extension, not a confirmed infection count.
Sources
- Instagram reel: https://www.instagram.com/reel/DgBfEL7iXnv/
- Threads post: https://www.threads.com/@dataeng.ai/post/DgBfMV0pDUa
- The Hacker News, Nov 10, 2026: https://thehackernews.com/2026/11/fireworks-ai-breach-widens-to-expose.html
- The Hacker News, Nov 15, 2026: https://thehackernews.com/2026/11/stolen-fireworks-ai-key-led-to-cursor.html
- BleepingComputer, Nov 10, 2026: https://www.bleepingcomputer.com/news/security/fireworks-ai-discloses-new-breach-after-cloud-provider-hack/
This post started as an Instagram post →
- https://www.instagram.com/reel/DgBfEL7iXnv/
- https://www.threads.com/@dataeng.ai/post/DgBfMV0pDUa
- https://thehackernews.com/2026/11/fireworks-ai-breach-widens-to-expose.html
- https://thehackernews.com/2026/11/stolen-fireworks-ai-key-led-to-cursor.html
- https://www.bleepingcomputer.com/news/security/fireworks-ai-discloses-new-breach-after-cloud-provider-hack/
Numbers above trace to these sources. If one moved, tell us and we fix it.
Talk it through
Argue with us on Instagram.